Insight
Analysis and insights
Standards, threats and architectures for the security of corporate networks and industrial plants.
DLP and Shadow AI: protecting data when employees use artificial intelligence
Today DLP must control not only email and USB sticks, but also the prompts and files entered into artificial intelligence tools. Why it has become essential and how to introduce it…
PAM: controlled remote access for IT and OT, beyond the VPN
Vendors, technicians and administrators need remote access to systems. PAM lets you grant it in a controlled, tracked and time-limited way, in both IT and OT…
ISO27001 and NIS2: synergies and importance in industrial OT environments
Points of convergence ISO27001 certification and NIS2 compliance overlap in many ways in OT environments: Risk-based approach : Both adopt a…
MITRE ATT&CK Framework in the ICS world
The growing digitalisation of industrial control systems (ICS) has led to a significant increase in cybersecurity risks in critical sectors such as energy, manufacturing,…
EDR vs CLASSIC ANTIVIRUS
The new technology for defending against modern cyber threats is called EDR (Endpoint Detection and Response). What the characteristics of an EDR are Different vendors provide…
What is the NERC standard
The North American Electric Reliability Corporation (NERC) is a non-profit association that creates standards for securing important electrical facilities. NERC CIP…
Energy: the new target
A hacker group called Xenotime, described as “the most dangerous”, has a new target: the power grid. According to Dragos, a well-known security company, the…
The IEC 62443/ISA 99 standard
It is a fact that industrial plants are increasingly targeted by cyber attacks that are ever more specific and ever more dangerous. After Trisis/Triton, we are not talking about…
Lack of visibility in ICS systems
One of the main problems in an industrial network is the lack of network visibility. In other words, the objects connected to it are often unknown. If you try to ask a…
The greatest security risk is still human error
Several studies, including the Italian Cyber Security Report 2014, identify users’ lack of awareness among the main causes of vulnerability to cyber attacks…
The dark side of remote access to ICS/SCADA systems
You have probably experienced the convenience of connecting to industrial systems from the comfort of your armchair at home. Some may think that using software such as…
Botnet
Botnets were conceived as networks of computers to run and keep web services active. Criminals have compromised them to carry out fraudulent activities. Zombies of the Net…
The most dangerous ransomware of recent years
Malware created to demand a ransom has existed for years. Today it is called ransomware – the union of the words ransom and software. Not…
Malware
Malware, or malicious software, is software with harmful intent. Most online threats are malware of some kind. Everything you need to know Do you know how every year the…
SCADA: networks and security
Supervisory Control And Data Acquisition (SCADA) networks can be seen as a common control system used in…
Triton/TriSIS: the new Stuxnet
The recent discovery of ICS-specific malware targeting Schneider Electric’s Triconex safety instrumented systems (SIS). They have demonstrated the ability to…
Preventing human error
If you have read our article on the role of human error in cyber security breaches, you will know that human error is the main cause of over 90% of breaches.…
Responding to an ICS incident in 4 steps
Incident response in Information Technology (IT) and Operational Technology (OT) or Industrial Control Systems (ICS) may seem very similar, but it has several…
ICS security is not a copy and paste of IT systems
A large share of industrial control systems (ICS) are critical infrastructure underpinning our modern society. Some of them generate and distribute energy and heat to…
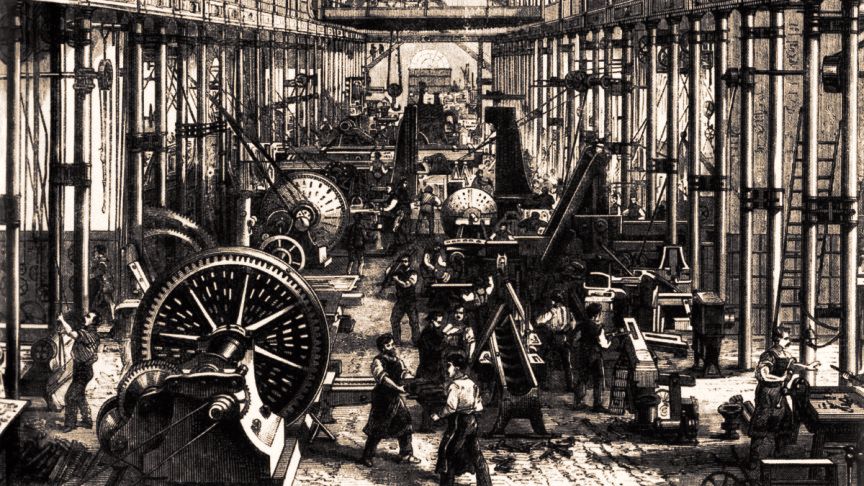
Through the Industrial Revolutions
Terms such as ICS, SCADA, ModBus, OT and IT are relatively recent. They were coined to regulate business processes in all those parts not related to…